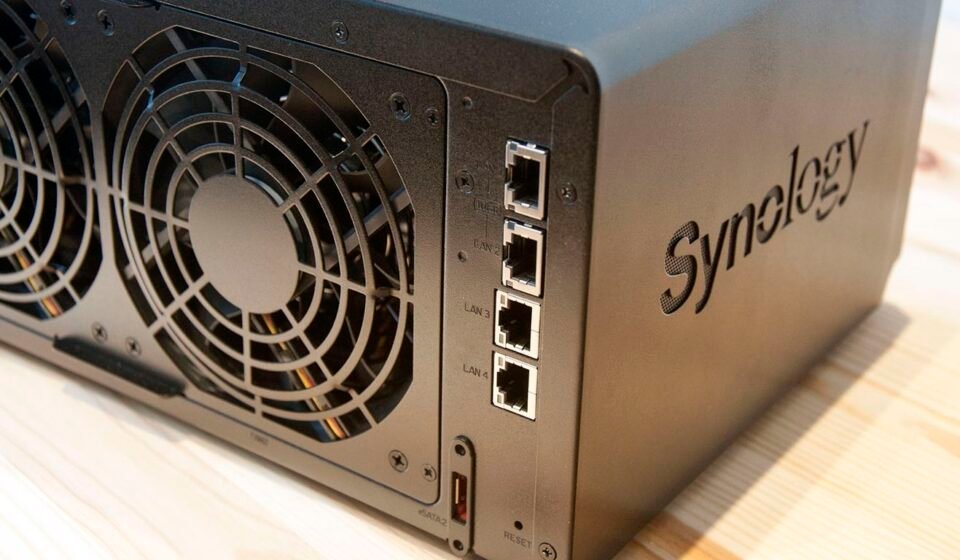

The PHP2Shell NAS vulnerability has turned a pair of critical PHP flaws into a problem for owners of internet-connected storage appliances. Tracked as CVE-2026-109618 and CVE-2026-109619, both bugs permit remote code execution. What began as a discussion about websites and web applications now reaches Network Attached Storage devices reachable from the public internet, as well as PHP-based Docker workloads. Patch coverage is uneven. Synology has issued updated PHP packages. QNAP has confirmed affected products but has no fix timeline. TerraMaster, Ugreen and Asustor are still developing fixes.
Two critical bugs, one expanding perimeter
The two CVEs are the core of the story. Each allows an attacker to run code remotely, which is the kind of access that matters most on a device holding files and running services. PHP underpins a large share of websites and web apps, and the affected versions are in wide use. The same runtime appears inside Docker containers that may run independently of the host NAS operating system. A device can therefore carry a vulnerable PHP build even if its main firmware is current.
Synology: which packages are affected
Synology’s advisory lists PHP 7.3 through 8.4, Mail Station and Synology Calendar as affected. The company has released updated PHP 8.2 and 8.4 packages, available through Package Center. Synology also draws a distinction between installed PHP packages and the PHP built into DiskStation Manager, stating that DSM’s built-in PHP is not exposed to the internet. Owners who installed PHP separately should check Package Center for the updated packages.
QNAP confirms affected products, fix pending
QNAP’s affected list is broader in product terms: QTS 5.2.11 and older, QTS 6.1.9, QuTS hero, QuTScloud and Note Station 3. A fix is in progress, but the company has not provided a timeline. QNAP reports no evidence of in-the-wild attacks on its devices. Its interim guidance is to remove devices from open internet access by disabling port forwarding, UPnP and remote-access services.
Other vendors still working
TerraMaster, Ugreen and Asustor are also working on fixes. No patch dates have been given for any of them. Owners of those brands should watch vendor advisories for model-specific updates. Devices that have reached end-of-life will not receive patches at all, which leaves network isolation as the remaining control.
Docker containers need a separate check
A NAS firmware update does not automatically fix PHP running inside a container. Docker users should verify the PHP version in each container and update where a vulnerable version is present. The exposure exists wherever the container’s PHP can be reached, regardless of the host operating system’s patch level.
Exploitation volume and an unexplained brake
Knowledge of the flaws leaked four days before patches were published, according to Amazon. Exploitation attempts climbed from hundreds measured 10 hours before publication to millions later. Most attempts appear unsuccessful. Researchers have suggested that address space layout randomization, or ASLR, may be impeding remote code execution. Whether ASLR fully explains the failure rate remains unclear, and no successful compromise of a NAS device has been confirmed.
What owners should do now
- Check the vendor’s security advisory for model-specific guidance.
- On Synology, update PHP 8.2 and 8.4 through Package Center and review Mail Station and Calendar exposure.
- Update PHP inside Docker container images where a vulnerable version runs.
- Remove the NAS from direct public internet access; disable port forwarding, UPnP and remote-access services.
- Use a VPN for remote access instead of forwarding management ports.
- Block unsolicited inbound connections at the network edge.
- Keep end-of-life devices local-only, since they cannot be patched.
The security community is urging immediate patching. For NAS owners, the practical question is not only whether a fix exists for the firmware, but whether the PHP runtime reachable from the internet has been updated or taken out of reach.