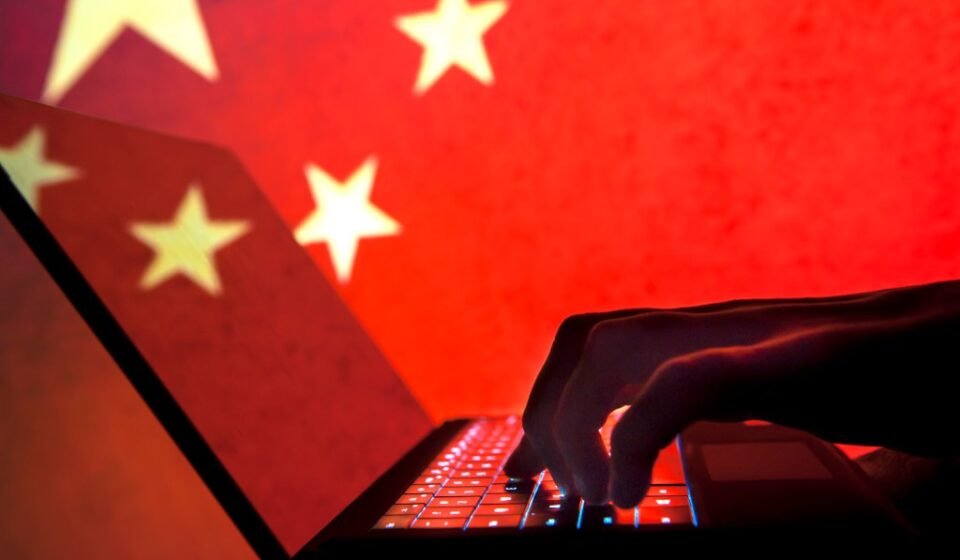

Microsoft security researchers have attributed a sprawling cyberespionage campaign to China state-aligned hackers who breached ConnectWise’s cloud backup service and gained access to roughly 2,250 customer organizations. The ConnectWise breach, disclosed in an article posted October 22, 2026, involved stolen application credentials that linked the IT management provider to its corporate customers and allowed the intruders to log into Microsoft-hosted environments as authorized users.
How the intrusion unfolded

The attackers first compromised ConnectWise’s cloud backup system, then stole application credentials that established data connections between ConnectWise and the companies it serves. Those credentials proved sufficient to authenticate into customers’ Microsoft-hosted environments, where the hackers accessed emails and other files while impersonating legitimate users. ConnectWise provides IT management and remote access services, and many customers rely on its cloud backup to store company data, making the service a high-value gateway for anyone seeking broad access.
Microsoft said the operation was carried out by actors aligned with the Chinese state. The company also said the intruders used AI agents to accelerate the campaign, driving almost 3,000 attempted sign-ins per minute. That volume left defenders with little time to detect and respond, according to Microsoft.
AI agents and the ARTEX framework

At the center of the speed and scale was an open-source AI framework called ARTEX, which works with AI models to stress-test cyber defenses. In this campaign, the same tooling was repurposed to attempt mass sign-ins across many organizations rapidly. Microsoft said the AI agents enabled the rapid intrusion into numerous networks, compressing what would normally be a slow, manual process into a high-velocity assault.
The brief does not specify how the application credentials were stolen, the exact date of the breach, whether data was exfiltrated or misused, or the full list of affected organizations. It also remains unclear whether ARTEX was modified for the attack or used as-is.
ConnectWise response and service restoration

ConnectWise said it paused access to its cloud backup system after discovering the breach and is investigating the incident. As of Thursday, the company was working to restore service. Whether that restoration is now complete has not been confirmed.
The company has not disclosed further details about the scope of the intrusion or the number of customers whose data may have been exposed. The affected organizations span thousands of companies that depend on ConnectWise for backup and remote access, a supply-chain position that magnifies the impact of any compromise.
A related incident in South Korea

The same AI software was used in a recent compromise of South Korea’s financial systems, according to the brief. Those systems were described as having weak security and lacking multi-factor authentication, which may have eased the attackers’ path. The specific financial institutions affected have not been identified.
The ConnectWise breach and the South Korea incident together point to a broader pattern: attackers are increasingly pairing stolen credentials with automated tools to probe and penetrate many targets at once. For defenders, the margin between detection and damage is shrinking.
Microsoft’s attribution to China state-aligned actors adds a geopolitical dimension to what is already a significant supply-chain security event. The investigation by ConnectWise continues, and customers await clarity on whether their data was accessed or exfiltrated.


[…] China-Linked Hackers Breach ConnectWise Cloud Backup, Spying on Thousands of Customers […]