
The PHP Foundation released patches on Wednesday for two critical vulnerabilities known as PHP2Shell, designated CVE-2026-109618 and CVE-2026-109619. The flaws permit unauthenticated remote code execution, meaning an attacker can run commands on a vulnerable system without any credentials. Patches are now public, but the window between early exploitation and disclosure has already produced confirmed compromises, and large numbers of systems are expected to stay exposed.
What the bugs allow

Remote code execution without authentication is among the most serious classes of server-side vulnerability. An attacker who reaches an unpatched PHP service can plant malware, steal data, and maintain a foothold inside the environment. Because PHP is open source, the patch details are public as well, giving defenders and attackers the same technical information.
From a 2024 discovery to a Wednesday patch
Researchers at Calif first identified the bugs in 2024 but did not regard them as exploitable at the time. A workable exploitation method was found later, prompting the researchers to alert the PHP Foundation. The foundation then ran a coordinated disclosure process with an embargo period, giving major companies early access to patches before the public release on Wednesday.
The embargo did not hold cleanly. The PHP Foundation blamed one company for releasing patches early. It remains unclear whether the early release was a leak, a communication breakdown, or something else, and the foundation has not publicly identified the company involved.
Exploitation before and after the patch
Amazon detected exploitation roughly a week before the patches became public, with the earliest evidence dated October 17. How the attacker learned of the vulnerabilities is not known. The possibilities include independent discovery and espionage, and the brief offers no conclusion.
After disclosure, Cloudflare CEO Matthew Prince reported an exponential number of exploitation attempts. By late Friday, Palo Alto Networks and Trail of Bits had confirmed compromises and post-exploitation activity. There is no evidence of mass exploitation so far, but the situation is not closed.
Why the blast radius is wide
Around 70% of the web-facing internet relies on PHP, and the language is decades old, free, and open source. It underpins WordPress, Drupal, Joomla, and MediaWiki, the software behind Wikipedia. PHP also runs in servers, developer tools, routers, firewalls, and VPNs, so the exposure is not confined to websites.
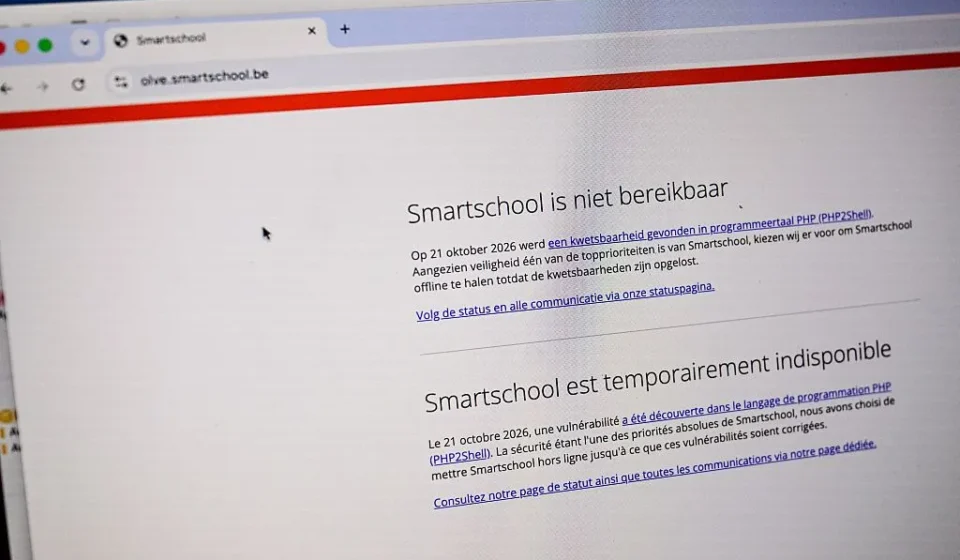
Industries took websites offline to apply patches, and governments urged citizens and companies to mitigate the risk. One visible example: Smartschool, an educational platform, was offline in Edegem on October 21, 2026. Smaller IT teams may update more slowly, and legacy systems that never receive patches could remain vulnerable for years.
AI's limited role, and the memory-safety problem underneath
Calif said AI assisted the exploitation work, but no model can find all bugs with simple prompts. The bulk of the effort relied on researcher knowledge. The incident nonetheless arrives as AI is expected to uncover more vulnerabilities over time.
The deeper issue is memory safety. PHP is memory-unsafe, and the National Security Agency says 75% of actively exploited vulnerabilities are memory-related. A move toward memory-safe languages such as Python, Rust, and Swift is underway, but that migration does not protect the PHP installations running today.
What remains unknown
The identity and scale of compromised targets are not public, and the full extent of exploitation has not been established. Whether mass exploitation will occur is also unresolved. The maintenance model adds strain: open-source maintainers are often unpaid and cannot afford security reviews, while companies that depend on PHP may not contribute financially. Against the backdrop of past internet-wide incidents such as the 2016 Dyn botnet, the 2017 NHS ransomware attack, and the 2024 CrowdStrike outage, the PHP2Shell episode is a reminder that a single widely used component can carry systemic risk.