France’s blood collection agency, Etablissement Français du Sang (EFS), has confirmed that a blood service fridge hack struck refrigeration units at three of its sites, but no biological materials were compromised. The intrusion, which affected equipment used to store blood products, was detected by the agency’s own monitoring systems, prompting staff to relocate the contents to secure storage before any loss occurred.
How the breach unfolded
The EFS reported that the attack originated not within its own infrastructure but through a service provider. Several outlets have identified that provider as Coolworld, a firm that maintains remote monitoring software for refrigeration systems. In a public notice, Coolworld attributed the incident to a component supplied by a third party, specifically pointing to its remote monitoring tool as the entry vector. The company has not released technical details, leaving unanswered whether the attackers exploited internet-facing equipment—a tactic observed in earlier assaults on supermarket freezer systems—or whether they first breached Coolworld’s internal network to reach the controllers.
One detail stands out: it was the EFS’s own alarm system, not the vendor’s, that flagged the anomaly. That sequence suggests the blood service’s monitoring remained functional even as the connected cooling units were compromised.
Regional impact and official response
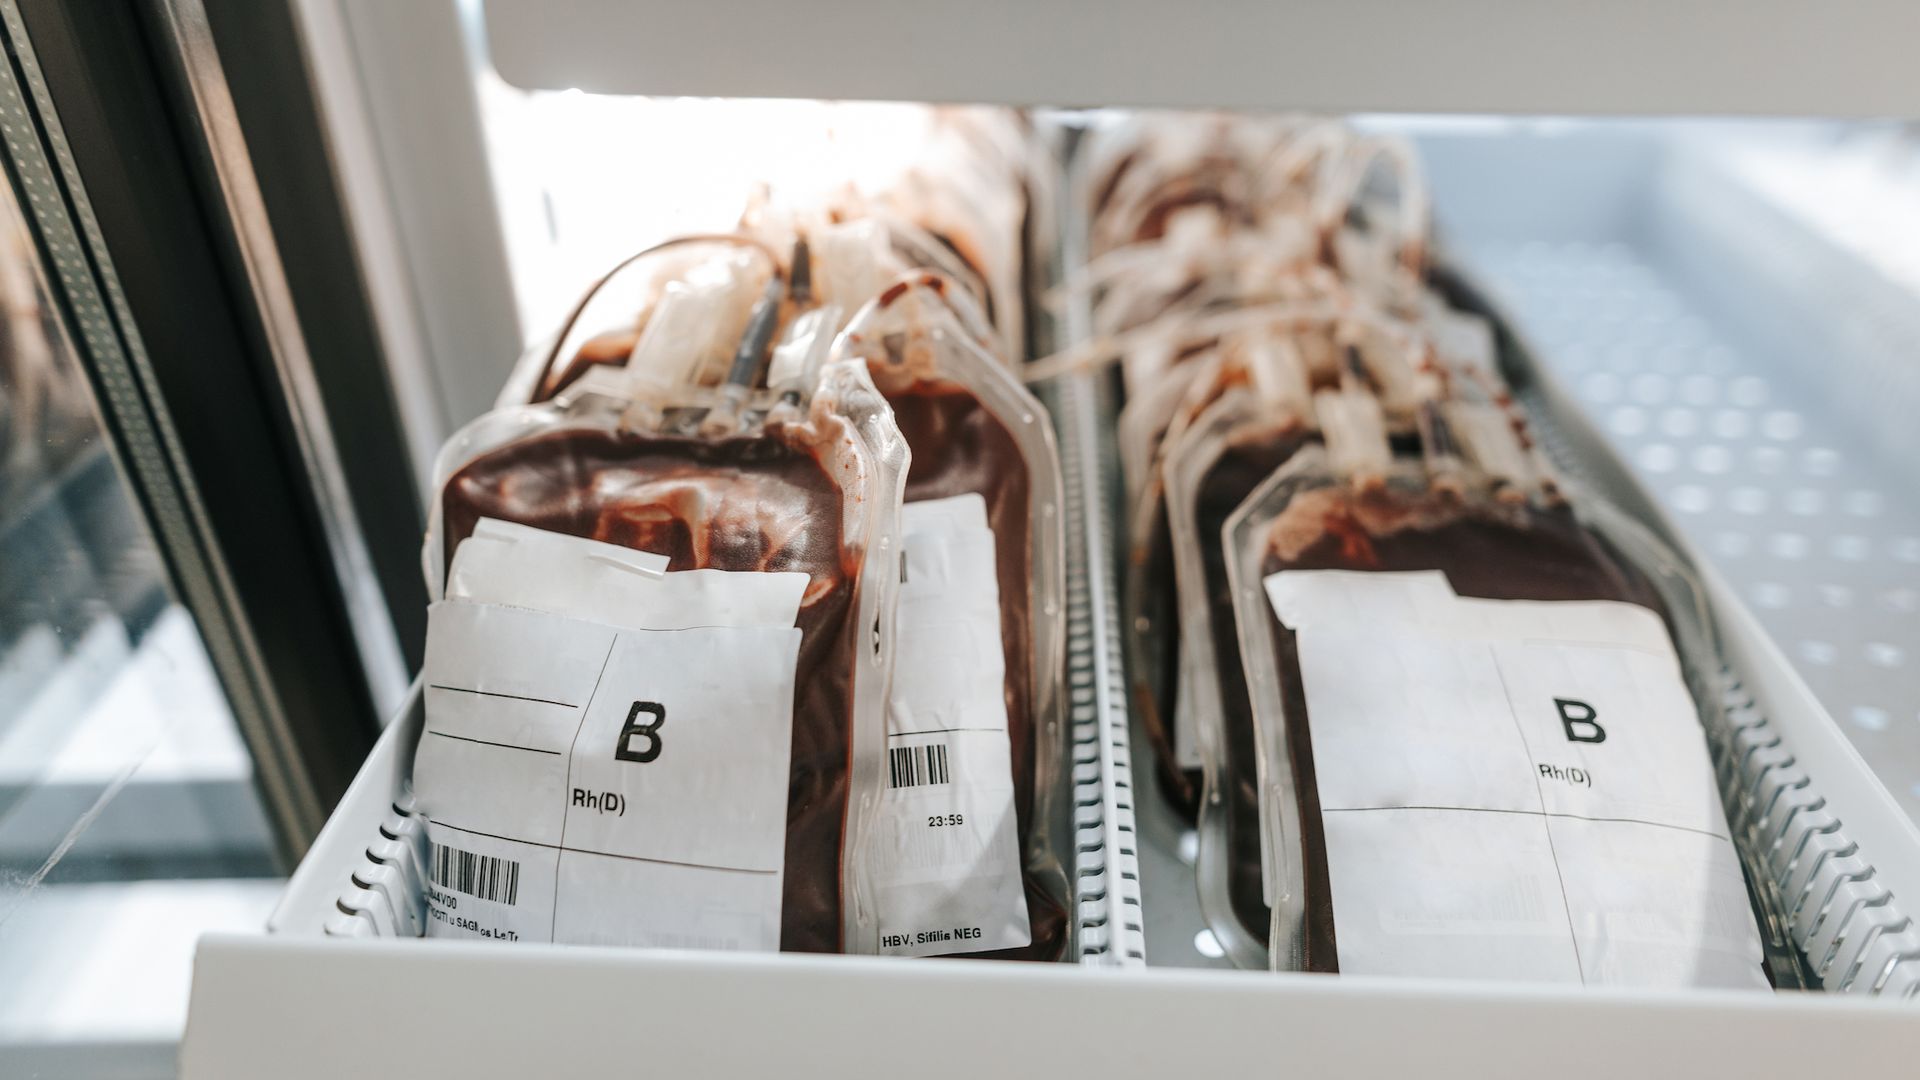
The French Health Ministry stated that the situation is under close surveillance and echoed the EFS in confirming that no assets were lost. The affected sites include one in the Burgundy-Franche-Comté region, though the full list of locations has not been disclosed. The EFS communiqué emphasized that the intrusion was limited to the service provider’s systems, reinforcing the agency’s position that its core operations and stored materials remained safe.
A pattern of refrigeration attacks
The EFS incident is the latest in a series of cyber intrusions targeting temperature-controlled units across Europe. Earlier waves in October and November focused on supermarket freezers, with attackers seemingly operating on a per-vendor basis. Danfoss controllers have been the most frequently mentioned in connection with those attacks, particularly around November 1–2, while Copeland/Dixell units were named in incidents on October 13–14.
Security guidance from the manufacturers has come under scrutiny. A Danfoss datasheet advises installing its controllers behind properly configured firewalls on a secure local network, and explicitly warns against exposing them to public or unsecured networks. The company issued a support bulletin in October 2026 recommending VPN usage—a document that appears to be a recent addition. For Copeland/Dixell, older manuals instructed installers to map ports 80 and 22 to the internet so the units could be reached remotely, offering VPN as merely an option. A security advisory published on October 14, after the first wave of attacks, revised that guidance to recommend VPN-only access.
Claimed responsibility and unresolved questions
Russia-aligned hacking groups Noname057(16) and Z-Pentest have reportedly claimed responsibility in Telegram posts that have since been deleted. Z-Pentest allegedly posted 2,500 lines of Danfoss code, but none of the purported materials have been publicly verified. The groups frame their attacks as a response to poor cybersecurity practices.
Whether the EFS breach followed the same playbook as the supermarket attacks remains unclear. If Coolworld kept its controllers inside its own network, the attackers would have needed to penetrate that network first—a more complex operation than scanning for exposed devices. The absence of technical disclosures from either Coolworld or the EFS leaves that question open.
What is evident is that the remote monitoring supply chain represents a vulnerable link. Third-party software connecting operational technology to the internet can bypass an organization’s own defenses, and the EFS case shows that even critical health infrastructure depends on vendors whose security posture may lag behind. For now, the blood service’s alarms worked as intended, but the broader lesson about connected cooling equipment is still being written.